All services
Penetration testing services by type
Every target needs a different test. Therefore this page lists our penetration testing services by type, so you can read about the one your auditor, customer or investor asked for.
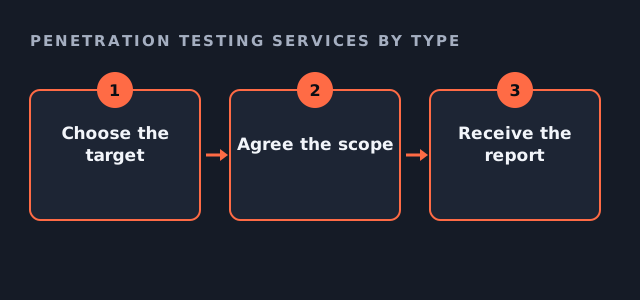
How to use these penetration testing services by type
Start with what was asked of you. For example, a SOC 2 auditor usually wants an application test and an external network test. A bank, however, may ask for an internal test as well. Each guide explains the scope, the method and what moves the price.
Not sure which test you need? Send us the request you received. We will read it. Then we tell you plainly what it requires.
What every one of our penetration testing services by type shares
The target changes, but the rules do not. First, nothing starts without written authorisation from the system owner. Second, every finding is reproduced by hand before it reaches the report. Third, one retest is included, so the final report can show closed issues.
In addition, each report follows a published method, such as the OWASP testing guide or NIST SP 800-115. As a result, an auditor can see exactly what was covered and how.
Applications and APIs
Products your customers log into. Also the endpoints behind them. Most SaaS buyers start here.
Networks and infrastructure
The edge comes first. Then the inside. Finally, the systems everything runs on.
Cloud platforms
Identity is the weak point. So these guides cover configuration on the three major providers.
Compliance and buying guides
Frameworks that ask for a test. Also, how to compare firms and prices.
Not sure which of our penetration testing services by type fits?
Send us the requirement in your customer's questionnaire or your auditor's request list, and we will map it to a written scope.
Get my estimate