Service
WordPress penetration testing for sites that matter to the business
WordPress penetration testing looks beyond the core software. So it focuses on plugins, themes, user roles and hosting, where most real weaknesses sit.
- Named tester before day one
- One retest within 30 days
- OWASP WSTG and NIST SP 800-115
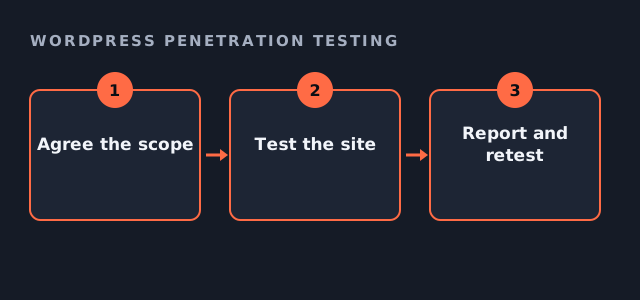
Why WordPress penetration testing is worth doing
WordPress core is maintained closely. However, a typical business site adds many plugins, a custom theme and integrations. Therefore the combination is unique, and an automated scan cannot judge it fully.
Sites that take payments, hold customer data or feed a CRM deserve a human look. Also, membership and learning sites carry account risk.
What WordPress penetration testing examines
The test covers the parts you control. For example, custom code and configuration.
- Plugins and themes, including custom ones
- User roles and access to the admin area
- Forms, uploads and integrations
- Hosting configuration and exposed files
- Authentication, including multi-factor setup
WordPress penetration testing readiness check
Tick what you can provide before testing.
Your result appears here as you tick, so you can see what is still open.
A scan compared with WordPress penetration testing
Both have a place. However, they answer different questions.
| Topic | Plugin scanner | Penetration test |
|---|---|---|
| Finds known plugin issues | Yes | Yes |
| Judges custom code and logic | No | Yes |
| Proves real impact | No | Yes, with evidence |
Authorisation and hosting
Testing runs only under your written authorisation. Also, managed hosts sometimes have their own rules, so we check them during scoping. As a result, testing stays inside every agreement.
In addition, a staging copy of the site is preferred for intrusive checks. Hardening advice is in the WordPress hardening guide.
Fees and timing
WordPress sites are web applications, so they fall within our published web application range of $5,000 to $30,000. One retest within 30 days is included, and a named tester is confirmed before day one.
Also plan for updates after the report. Because plugins change often, a fix today can regress next month. So keep a simple plugin inventory with owners, and remove plugins nobody uses. In addition, review admin accounts quarterly, because old agency logins often linger long after projects end.
WordPress penetration testing questions
Is WordPress penetration testing needed if we update plugins?
Updates help, but custom code, roles and configuration still need testing.
Does WordPress penetration testing cover the host?
Hosting configuration is reviewed, within what your host allows.
What does WordPress penetration testing cost?
It falls within our web application range of $5,000 to $30,000, depending on scope.
Is a retest included?
Yes. One retest within 30 days is included.
Related guides
Scope your WordPress penetration testing
Tell us about the site, its plugins and its host. We reply with a written estimate, usually within four working hours.
Get my estimate