Service
Azure penetration testing, with identity at the centre
Azure penetration testing looks at your tenant and subscriptions the way an attacker would. Because Azure and Microsoft 365 share one identity layer, a weak account in one often opens the other.
- Named tester before day one
- One retest within 30 days
- OWASP WSTG and NIST SP 800-115
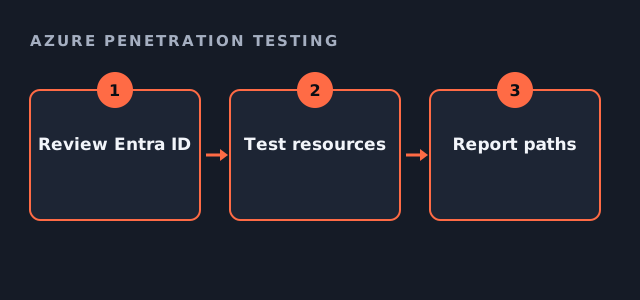
What Azure penetration testing covers
Identity is the control plane in Azure. Therefore we start with Entra ID and follow the permissions outwards.
- Privileged role assignments and who can grant them
- Service principals, app registrations and their secrets
- Storage accounts, key vaults and shared access signatures
- Network security groups and exposed management endpoints
- Conditional access gaps that let risky sign-ins through
Microsoft's rules for Azure penetration testing
Microsoft allows customers to test their own resources without notice, within its published rules. It forbids denial of service and attacks on other tenants. The Microsoft Cloud penetration testing rules of engagement sets out the details, and we reference them in your authorisation.
Azure penetration testing checklist
Tick what is already true. It tells us how quickly the scope can be fixed.
Your result appears here as you tick, so you can see what is still open.
From one account to the subscription
The question we try to answer is simple: if one user or one app secret leaked, how far could it go? For example, a service principal with contributor rights across subscriptions can often read every key vault. Showing that chain is what makes the report useful to your engineers.
How Azure penetration testing is delivered
We begin with a read-only review using an account you create. Then we test agreed paths actively, inside agreed windows. Each finding is written up with proof and a fix, and one retest inside 30 days is included. You also receive a short attestation letter for customers.
Price range for Azure penetration testing
Azure work sits inside our published cloud range of $10,000 to $50,000. The number of subscriptions and the size of the tenant move it most. A single subscription sits low; however, a large tenant with many app registrations sits higher.
Azure penetration testing questions
Does Azure penetration testing include Microsoft 365?
It can. Because both share Entra ID, many clients scope them together. If you only need one, we scope only that one.
Do we need to notify Microsoft?
Not for testing your own resources within the published rules. We confirm the current rules with you.
Will Azure penetration testing lock out users?
We avoid it. Password attacks are agreed in advance and kept well below lockout thresholds.
Can you test a single subscription?
Yes. Scope can be one subscription, a management group or the whole tenant.
Related guides
Request an Azure penetration testing scope
Tell us the size of the tenant and the number of subscriptions. We reply in writing with scope and fee.
Get my estimate