Compliance testing
ISO 27001 penetration testing that maps to your risk assessment
ISO 27001 penetration testing is not mandated by name. Instead, the standard expects you to manage technical vulnerabilities and test security in development, and most certification auditors expect a test as evidence.
- Named tester before day one
- One retest within 30 days
- OWASP WSTG and NIST SP 800-115
What ISO 27001 actually requires
The ISO/IEC 27001 standard is risk-based. It does not say you must commission a penetration test. However, Annex A controls 8.8 (management of technical vulnerabilities) and 8.29 (security testing in development and acceptance) are hard to evidence without one.
Scoping ISO 27001 penetration testing from your risk register
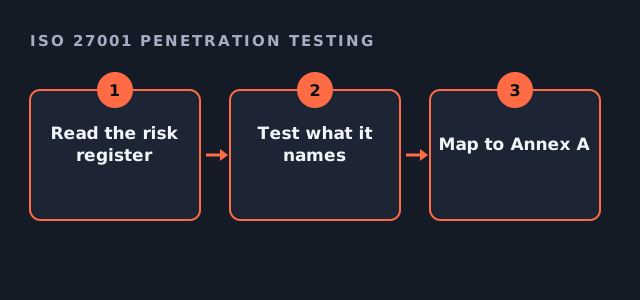
Because the standard is risk-driven, the test should follow your own risk assessment. For example, if your register names the customer portal and remote access as high risks, those become the targets. As a result, the scope is easy to defend to an auditor.
ISO 27001 penetration testing readiness
Tick what you already have. Each item makes the scope easier to defend.
Your result appears here as you tick, so you can see what is still open.
Which Annex A controls the test supports
The report can be referenced against several controls. The table shows the common ones.
| Control | How a test supports it |
|---|---|
| 8.8 Technical vulnerabilities | Shows vulnerabilities were identified and fixed. |
| 8.29 Security testing | Evidence that new systems were tested before release. |
| 8.20 Network security | External and internal tests show network controls work. |
| 5.7 Threat intelligence | Findings feed back into your threat picture. |
How often to repeat ISO 27001 penetration testing
The standard sets no fixed interval. Most organisations test annually and after significant changes, which aligns with surveillance audits. If your risk assessment says otherwise, follow it and record why.
What you receive
You receive a report with the scope, method, findings and fixes, plus an attestation letter. In addition, we add a short mapping of findings to Annex A controls so your internal audit team can file it directly. One retest inside 30 days is included.
ISO 27001 penetration testing questions
Is ISO 27001 penetration testing mandatory?
Not by name. The standard is risk-based, but most auditors expect a test as evidence for technical vulnerability controls.
Can the certification body perform the test?
Generally not, because it must stay independent of what it certifies.
Does ISO 27001 penetration testing replace vulnerability scanning?
No. Scanning is continuous, while a test is periodic and deeper. Auditors usually like to see both.
Which targets should we test?
The ones your risk assessment rates highest, typically customer-facing apps and remote access.
Related guides
Scope ISO 27001 penetration testing from your risk register
Send us the relevant risks and your audit date. We reply with a written scope and a fixed fee.
Get my estimate