Service
Infrastructure penetration testing for the systems everything else runs on
Infrastructure penetration testing covers the servers, directory services, remote access and network devices beneath your applications. So if those fall, every application on top falls with them.
- Named tester before day one
- One retest within 30 days
- OWASP WSTG and NIST SP 800-115
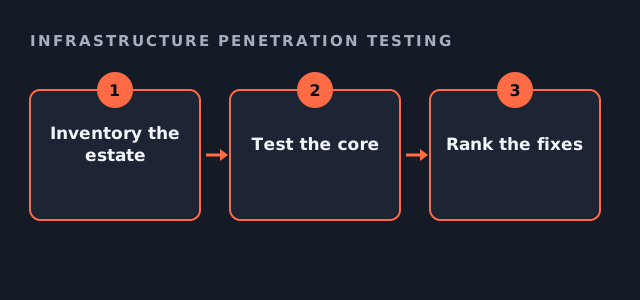
What infrastructure penetration testing includes
Infrastructure is the shared layer. Therefore a single weakness here often affects many systems at once.
- Directory services and the accounts they manage
- Servers, both Windows and Linux
- Remote access gateways and VPNs
- Network devices, such as firewalls and switches
- Backup and management systems that hold broad access
Directory services deserve special attention
In most organisations the directory controls who can log in to everything. As a result, a weak service account or an old delegation setting can lead from one user to full control. Therefore infrastructure penetration testing spends real time mapping those paths.
Infrastructure penetration testing checklist
Tick what you can provide. It sets the scope and the safety rules.
Your result appears here as you tick, so you can see what is still open.
How it relates to network testing
Network testing focuses on reachability and exposure. By contrast, infrastructure testing goes deeper on the core services once they are reached. Many clients also scope them together.
| Network test | Infrastructure test | |
|---|---|---|
| Main question | What can be reached? | What can be taken over? |
| Focus | Hosts, ports and exposure. | Directory, servers and management planes. |
| Published range | $4,000 to $35,000 depending on side. | Scoped from the same ranges. |
How infrastructure penetration testing is kept safe
Core systems cannot go down during a test, so we agree windows, exclusions and a stop procedure in writing, and avoid any destructive step without separate approval. The method follows NIST SP 800-115.
What you receive
You receive findings ranked by how much of the estate each one exposes, with proof and a fix. In addition, there is an executive summary and an attestation letter. One retest inside 30 days is included.
Infrastructure penetration testing questions
Is infrastructure penetration testing internal or external?
Both are possible, but most of the depth comes from the internal view, starting from an agreed foothold.
Will it disrupt our servers?
We design it not to, so risky steps need separate written approval and are scheduled with you.
Does infrastructure penetration testing include the cloud?
It can include cloud-hosted servers, while cloud identity and configuration are usually scoped as a cloud test.
How long does it take?
Hands-on work runs three to ten days depending on size, followed by the report.
Related guides
Scope infrastructure penetration testing
Send us a rough inventory and your constraints. We reply with a written scope and a fixed fee.
Get my estimate