Service
Mobile app penetration testing for iOS and Android
Mobile app penetration testing looks at two things: what your app leaves on the device, and how it talks to your backend when nobody is watching. Both matter, because a phone is a device you do not control.
- Named tester before day one
- One retest within 30 days
- OWASP WSTG and NIST SP 800-115
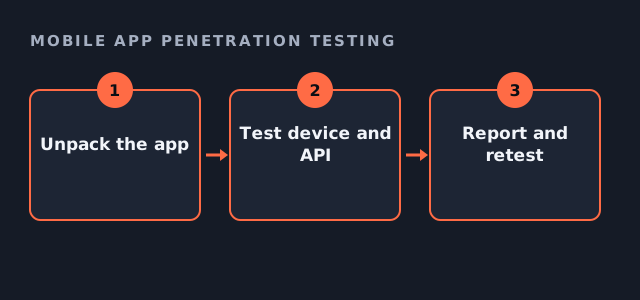
What mobile app penetration testing covers
The app itself is only half the story. Therefore we test the build and the backend it depends on.
- Data stored on the device, including tokens and cached records
- Communication with the backend, including certificate checks
- Authentication, session handling and biometric shortcuts
- Tampering, debugging and reverse engineering resistance
- The API calls the app makes, and the ones it could make
A recognised method
Our checks follow the OWASP Mobile Application Security project, which covers both iOS and Android. As a result, your auditor or customer can match each finding to a published requirement.
Mobile app penetration testing checklist
Tick what you can supply. It decides how fast testing can start.
Your result appears here as you tick, so you can see what is still open.
iOS and Android differences
The platforms store data and enforce permissions differently, so each build is tested on its own.
| Area | iOS | Android |
|---|---|---|
| Local storage | Keychain and app sandbox. | Keystore, shared preferences and external storage. |
| Inter-app links | URL schemes and universal links. | Intents, deep links and exported components. |
| Typical issue | Sensitive data in backups or logs. | Exported components other apps can call. |
How mobile app penetration testing is scoped
We need the builds, a test account for each role, and the API environment the app calls. The number of platforms and roles drives the effort. In addition, an app with payments or health data needs deeper backend testing.
Price range and report
Our published range is $5,000 to $40,000. One platform with a simple backend sits low; both platforms with several roles and a large API sit higher. The report includes proof and fixes for each finding, an executive summary, an attestation letter and one retest inside 30 days.
Mobile app penetration testing questions
Do you need the source code for mobile app penetration testing?
No. We test the compiled builds, as an attacker would. Source access can make some checks faster.
Can you test both platforms at once?
Yes. Each is tested separately, but the backend is shared, so combined scopes are efficient.
Is the backend API included in mobile app penetration testing?
The calls the app makes are included. A full API test of every endpoint can be added.
Do you test on jailbroken devices?
Yes, because attackers do. It shows what your app exposes when the device itself is not trustworthy.
Related guides
Get a fixed fee for mobile app penetration testing
Tell us the platforms, the roles and what the app does. We reply with a written scope and a fee.
Get my estimate