Compliance testing
HIPAA penetration testing for systems that hold patient data
HIPAA penetration testing helps covered entities and business associates show that safeguards around electronic protected health information actually work. The Security Rule does not name the test, but your risk analysis usually calls for it.
- Named tester before day one
- One retest within 30 days
- OWASP WSTG and NIST SP 800-115
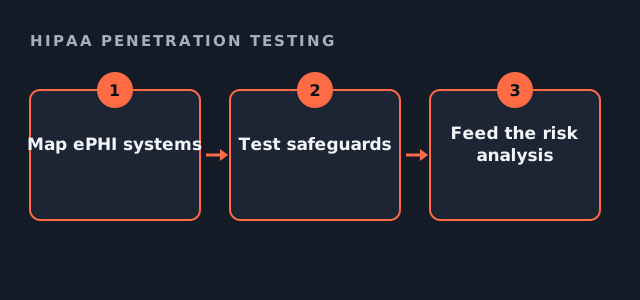
Where HIPAA penetration testing fits
The HIPAA Security Rule requires an accurate risk analysis and ongoing evaluation of safeguards. However, it does not say how. So a penetration test is a clear way to show safeguards work in practice. The HHS guidance on risk analysis explains what a risk analysis should cover.
What HIPAA penetration testing should include
Start from where electronic protected health information lives and flows. Then test the paths into it, because that is how an attacker would reach the records.
- Patient portals and clinician web applications
- APIs that exchange records with partners
- Remote access used by staff and vendors
- Cloud storage holding records or backups
- Internal networks where clinical systems sit
HIPAA penetration testing checklist
Tick what is true for you. It shows which systems belong in scope.
Your result appears here as you tick, so you can see what is still open.
Keeping HIPAA penetration testing safe around health data
We agree in writing how test data is handled. For example, we prove access to records without downloading them, and we stop at the first proof. Also, any real patient data seen during testing stays inside the agreed rules, and nothing is retained.
How HIPAA penetration testing feeds your risk analysis
Each finding is rated by likelihood and impact, which is the language a risk analysis uses. Consequently, your compliance lead can move findings straight into the risk register and track fixes. One retest inside 30 days confirms the most important ones.
Scope and price
There is no special HIPAA price, so each target uses our published ranges. For example, a web application is $5,000 to $30,000. Most health technology companies combine an application and an external test.
HIPAA penetration testing questions
Does HIPAA require penetration testing?
Not by name. The Security Rule requires risk analysis and evaluation of safeguards, and a test is a common way to meet that.
Will you sign a business associate agreement?
Where testing could expose ePHI, we discuss one during scoping and agree data handling rules in writing.
How often should HIPAA penetration testing happen?
Annually is common, but also after significant changes to systems that hold ePHI.
Can testing avoid real patient data?
Yes, ideally, so staging with synthetic data is preferred, while read-only checks in production where needed.
Related guides
Scope HIPAA penetration testing for your systems
Tell us where ePHI lives and who asked for the test. We reply with a written scope and a fixed fee.
Get my estimate