Service
SaaS penetration testing built around tenant isolation
SaaS penetration testing answers the question every enterprise buyer asks: can one customer ever see another customer's data? It combines application, API and cloud testing around that single risk.
- Named tester before day one
- One retest within 30 days
- OWASP WSTG and NIST SP 800-115
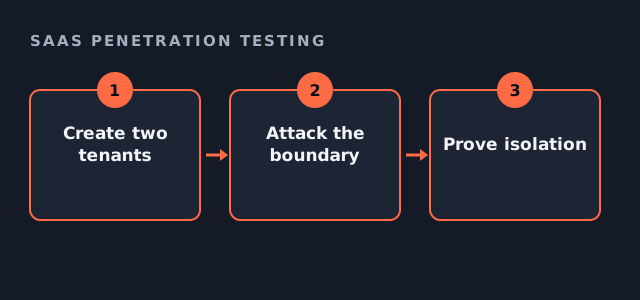
Why SaaS penetration testing is different
In a multi-tenant product, the worst finding is not a crash. Instead, it is one tenant reading or changing another tenant's records. So we set up at least two tenants and spend much of the test trying to cross between them.
What SaaS penetration testing covers
The scope usually joins several targets into one engagement.
- Tenant isolation in the application and the API
- Role permissions inside each tenant
- Single sign-on, invitations and account linking
- File storage, exports and shared links
- The cloud configuration that hosts it all
SaaS penetration testing readiness
Tick what you can set up. Two tenants matter most.
Your result appears here as you tick, so you can see what is still open.
What enterprise customers and auditors ask for
Security questionnaires usually ask for an annual independent test, the date, the scope and the status of findings. Similarly, SOC 2 auditors expect to see one. The report and attestation letter answer both without sharing the details.
| Asked by | What they want |
|---|---|
| Enterprise customer | Date, scope and confirmation that high findings are fixed. |
| SOC 2 auditor | Independent test, method and remediation evidence. |
| Investor | Assurance that tenant data is isolated. |
How SaaS penetration testing is scoped
We count tenants, roles, features and API endpoints. Then we decide whether cloud configuration belongs in the same engagement. Combining them is often cheaper than separate tests, because the tester learns the system once.
Price and timing
SaaS work combines our published ranges: $5,000 to $30,000 for the application, $10,000 to $25,000 for an API, and $10,000 to $50,000 for cloud. Most SaaS companies land between $10,000 and $30,000 overall. Hands-on testing runs three to ten days, and one retest inside 30 days is included.
SaaS penetration testing questions
How often do enterprise customers expect SaaS penetration testing?
Most ask for an annual independent test, plus confirmation that high findings were fixed.
Can we share the full report with customers?
You can, but most share the attestation letter instead, which confirms the test without exposing details.
Is SaaS penetration testing enough for SOC 2?
It provides strong evidence. Your auditor still tests your other controls separately.
Do you test single sign-on?
Yes, because invitations and account linking are common places for tenant boundaries to break.
Related guides
Get a SaaS penetration testing scope
Tell us your tenants, roles and deadline. We reply with a written scope and a fixed fee.
Get my estimate