Service
Oracle Cloud penetration testing for OCI tenancies
Oracle Cloud penetration testing looks at your Oracle Cloud Infrastructure tenancy the way an attacker would. So it covers identity, network rules, storage and the workloads you run.
- Named tester before day one
- One retest within 30 days
- OWASP WSTG and NIST SP 800-115
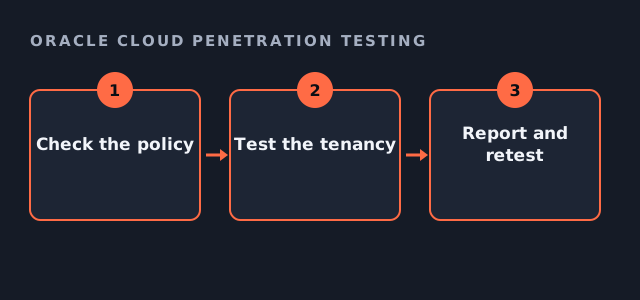
Oracle's rules for Oracle Cloud penetration testing
Oracle publishes a cloud security testing policy. Therefore testing follows its permitted activities, and it targets your resources rather than Oracle's shared platform.
We check the current policy during scoping. Also, rules of engagement record which accounts and regions are in scope.
What Oracle Cloud penetration testing examines
Most cloud breaches start with configuration. For example, an overly broad policy or a public bucket.
- Identity policies, groups and compartments
- Network security lists and gateways
- Object storage visibility
- Exposed compute and database services
- Logging and audit settings
Oracle Cloud penetration testing readiness check
Tick what you can provide.
Your result appears here as you tick, so you can see what is still open.
Scoping Oracle Cloud penetration testing
Tenancy size drives effort. However, structure matters as much.
| Question | Effect on scope |
|---|---|
| How many compartments? | Each adds policy review |
| Which regions? | Multi-region adds coverage |
| Managed databases in use? | Database exposure is reviewed |
| Hybrid connections? | On-premises links widen scope |
Authorisation and evidence
Testing runs only under your written authorisation, inside Oracle's policy. As a result, nothing touches resources you do not own.
Findings come with evidence and a fix. The report also suits auditors, so an attestation letter can be shared with customers. Oracle's rules are in the Oracle Cloud security testing policy.
Fees and timing
Cloud configuration testing sits within our published range of $10,000 to $50,000. One retest within 30 days is included, and a named tester is confirmed before day one.
Also review compartments regularly. Because teams create resources quickly, policies written for one project often grow wider over time. So a short quarterly review of policies keeps access close to need. In addition, enable audit logs across all regions in use, because gaps there make incidents hard to investigate.
Oracle Cloud penetration testing questions
Does Oracle require approval for Oracle Cloud penetration testing?
Oracle publishes a testing policy that sets permitted activities, so we check it during scoping.
Does Oracle Cloud penetration testing include databases?
Exposure of managed databases is reviewed when they are in scope.
What does Oracle Cloud penetration testing cost?
It sits within our cloud range of $10,000 to $50,000, depending on scope.
Is a retest included?
Yes. One retest within 30 days is included.
Related guides
Scope your Oracle Cloud penetration testing
Tell us about your tenancy, compartments and regions. We reply with a written estimate, usually within four working hours.
Get my estimate