Service
Docker penetration testing for containerised applications
Docker penetration testing checks whether your containers keep their promises of isolation. So it looks at images, runtime settings, secrets and the host underneath.
- Named tester before day one
- One retest within 30 days
- OWASP WSTG and NIST SP 800-115
Why Docker penetration testing matters
Containers package software neatly. However, a container running with too many privileges can expose the host. Therefore configuration matters as much as the application inside.
Teams also move fast with containers. Also, images pulled from public registries can carry old components nobody reviewed.
What Docker penetration testing examines
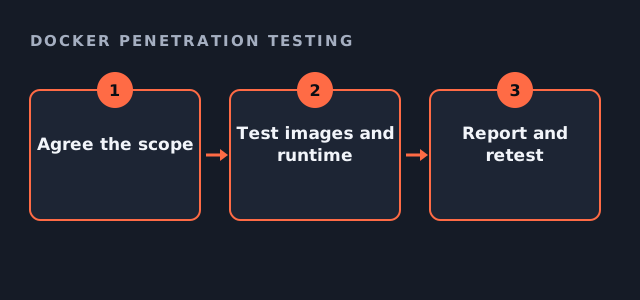
The test moves from build to runtime. For example, what the image contains and how the container runs.
- Image contents and outdated components
- Privileges, capabilities and user settings
- Secrets in images or environment variables
- Exposed daemon or management interfaces
- Network exposure between containers
Docker penetration testing readiness check
Tick what you can provide.
Your result appears here as you tick, so you can see what is still open.
Scoping Docker penetration testing
Scope depends on where containers run. However, a few facts settle most estimates.
| Question | Effect on scope |
|---|---|
| How many images and services? | More images, more review |
| Single host or orchestrated? | Orchestration adds layers |
| Which registry? | Registry access is reviewed |
| Cloud or on-premises? | Cloud provider rules apply |
Authorisation and safety
Testing runs only under your written authorisation. Also, a non-production environment is preferred for runtime checks. As a result, live services are not disturbed.
Findings come with evidence and a fix, mapped to guidance such as the OWASP Docker Security Cheat Sheet.
Fees and timing
Container work is priced after scoping, often alongside cloud configuration testing. Most companies land between $10,000 and $30,000, and the exact figure follows scope. One retest within 30 days is included, and a named tester is confirmed before day one.
Also review the build pipeline. Because images are rebuilt often, a fix in one image can disappear in the next build. So bake the fix into the base image and the pipeline, not only the running container. In addition, rebuild images on a schedule, because base layers age quickly even when your code does not change.
Docker penetration testing questions
Is Docker penetration testing the same as image scanning?
No. Scanning finds known issues, while a test shows real impact with evidence.
Does Docker penetration testing include Kubernetes?
Only if agreed in scope, because orchestration adds its own surface.
Can Docker penetration testing run in production?
It can, but a test environment is safer.
Is a retest included?
Yes. One retest within 30 days is included.
Related guides
Scope your Docker penetration testing
Tell us how many images you run and where. We reply with a written estimate, usually within four working hours.
Get my estimate