Service
API penetration testing for the endpoints your product really runs on
API penetration testing checks whether each endpoint enforces who may see and change what. Increasingly, the API is the whole product, so a single broken check can expose every customer's data.
- Named tester before day one
- One retest within 30 days
- OWASP WSTG and NIST SP 800-115
Why API penetration testing is its own test
Web front ends hide a lot. However, the API behind them accepts anything a client sends, including requests the interface never makes. That is why the most serious findings in modern apps sit in the API layer.
What API penetration testing checks
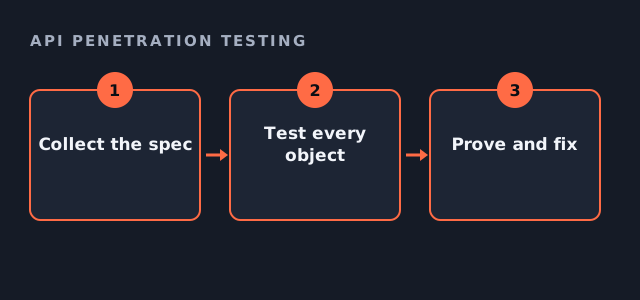
We work from your specification, such as an OpenAPI file or a Postman collection, and then go beyond it.
- Object references you can walk, such as changing an ID in the URL
- Function-level checks, such as a user calling an admin endpoint
- Excessive data returned to the client
- Rate limits that are missing or easy to bypass
- Mass assignment of fields the user should not set
The checklist follows the OWASP API Security Top 10, which auditors recognise.
API penetration testing readiness check
Tick what you can hand over. Missing items just become scoping questions.
Your result appears here as you tick, so you can see what is still open.
How API penetration testing is scoped
The fee depends on the number of endpoints and roles. Therefore we ask for the specification and a test account for each role. Undocumented endpoints we discover are reported too, because they are often the forgotten ones.
| Scope input | Why it matters |
|---|---|
| Number of endpoints | Every endpoint needs its own authorisation checks. |
| User roles | Each role multiplies the permission tests. |
| Authentication method | Tokens, keys and OAuth flows each need testing. |
| Versions in use | Old versions often lack newer checks. |
What you receive from API penetration testing
Every finding includes the exact request and response that prove it, plus a fix. In addition, you get an executive summary for leadership and an attestation letter for customers. One retest inside 30 days is included.
Price range
Our published range for API work is $10,000 to $25,000. A small internal API with one role sits near the bottom. On the other hand, a public API with partner keys and many roles sits near the top.
API penetration testing questions
Do you test GraphQL as part of API penetration testing?
Yes. GraphQL needs extra checks for introspection, query depth and field-level authorisation.
What if we have no specification?
We can work from traffic captured while using the app, although a specification makes the scope more precise.
Is API penetration testing included in a web app test?
Partly. A web test covers the calls the front end makes. A dedicated API test covers every endpoint, including the ones the interface never uses.
Can you test partner or public APIs?
Yes, if you own them or hold written authorisation from the owner.
Related guides
Get an API penetration testing quote in writing
Send the specification and the list of roles. We reply with a fixed fee and a written scope.
Get my estimate