Service
GraphQL penetration testing for APIs that expose a single endpoint
GraphQL penetration testing adapts API testing to one flexible endpoint. So it focuses on authorisation inside resolvers, schema exposure and limits on expensive queries.
- Named tester before day one
- One retest within 30 days
- OWASP WSTG and NIST SP 800-115
Why GraphQL penetration testing differs from REST testing
A REST API spreads functions across many endpoints. In contrast, GraphQL puts them behind one, and clients choose the shape of each response. Therefore access checks must work field by field.
Teams often secure the endpoint but not each resolver. As a result, a user may request fields they should never see.
What GraphQL penetration testing examines
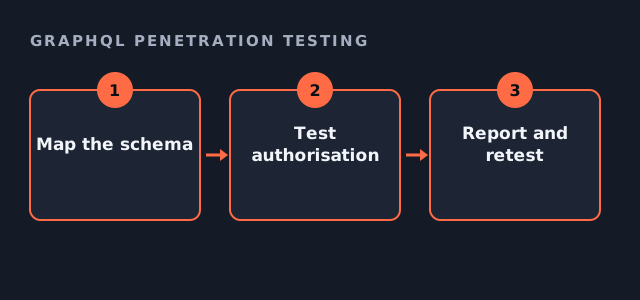
The test starts with the schema. Then it checks how each type and field is protected.
- Authorisation in resolvers and nested fields
- Schema exposure in production
- Limits on query depth and cost
- Input handling in mutations
- Error messages that reveal internals
GraphQL penetration testing readiness check
Tick what you can provide.
Your result appears here as you tick, so you can see what is still open.
Scoping GraphQL penetration testing
Schema size and roles drive effort. However, other factors matter too.
| Question | Effect on scope |
|---|---|
| How many types and mutations? | Larger schemas take longer |
| How many user roles? | Each role multiplies checks |
| Federated or single service? | Federation adds boundaries |
| Public or private API? | Public exposure widens risk |
Authorisation and safety
Testing runs only under your written authorisation. Also, mutations can change data, so a staging environment is preferred.
Findings come with evidence and a fix. Guidance such as the OWASP GraphQL Cheat Sheet helps engineers apply them.
Fees and timing
GraphQL work falls within our published API range of $10,000 to $25,000. One retest within 30 days is included, and a named tester is confirmed before day one.
Also consider how clients are built. Because mobile apps ship with queries inside them, an attacker can read those queries and adapt them. So treat every field as reachable, whatever the official client requests. In addition, log unusual query shapes, because they often signal probing before an attack.
GraphQL penetration testing questions
Is GraphQL penetration testing part of API testing?
Yes, with extra checks for resolvers, schema exposure and query limits.
Do we need to share the schema for GraphQL penetration testing?
It helps, because grey-box testing covers more within the same time.
What does GraphQL penetration testing cost?
It falls within our API range of $10,000 to $25,000, depending on scope.
Is a retest included?
Yes. One retest within 30 days is included.
Related guides
Scope your GraphQL penetration testing
Tell us about the schema, roles and environments. We reply with a written estimate, usually within four working hours.
Get my estimate