Service
AWS penetration testing focused on IAM, data and exposure
AWS penetration testing examines what you have built on Amazon Web Services, not Amazon itself. In practice, that means identity and access management, storage, keys and the network rules around your workloads.
- Named tester before day one
- One retest within 30 days
- OWASP WSTG and NIST SP 800-115
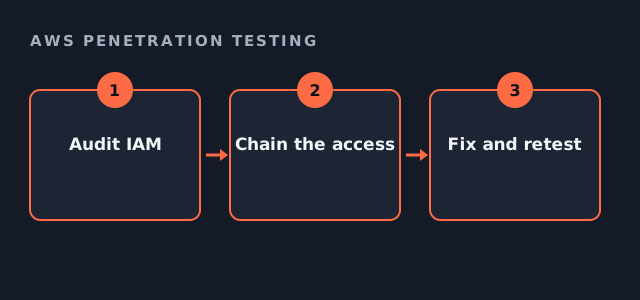
Where AWS penetration testing finds real problems
Most AWS incidents begin with something small. For example, an access key in a public repository, a role trusted by too many services, or an S3 bucket shared for one afternoon and never closed. So we look at identity first.
- IAM users, roles and trust policies
- S3 buckets, snapshots and public AMIs
- Secrets in Lambda, ECS task definitions and build systems
- Security groups and exposed management ports
- Cross-account access and organisation guardrails
What Amazon allows you to test
Amazon lets customers test many services without asking first, but it forbids denial of service and attacks on its shared infrastructure. The AWS penetration testing policy lists the details. Therefore we write your scope inside it and quote it in the authorisation.
AWS penetration testing readiness
Tick what you can provide. Open items are fine; they simply join the scoping questions.
Your result appears here as you tick, so you can see what is still open.
How AWS penetration testing runs
First, you create a read-only audit role, which lets us review the configuration safely. Next, we take one low-privilege identity and see how far it can go. Finally, we report each path with the exact policy line that allowed it. As a result, your engineers fix the cause rather than one symptom.
AWS penetration testing for audits and customers
SOC 2 auditors and enterprise customers often ask whether your cloud environment was tested by an independent party. The report and the short attestation letter answer that question. Neither, however, replaces your own monitoring or the controls your auditor tests.
Price and timing
Cloud work sits in our published range of $10,000 to $50,000. A single account with a handful of services sits near the bottom. In contrast, an AWS Organization with many accounts sits higher. Hands-on testing runs three to ten days, with one retest inside 30 days included.
AWS penetration testing questions
Do we need Amazon's approval for AWS penetration testing?
Not for the services Amazon lists as permitted. We check the current policy with you during scoping.
Can you test AWS without production access?
Yes. Many clients give us a staging account that mirrors production, then a read-only role in production for configuration review.
Does AWS penetration testing include our application?
Only if you add it. Application testing is scoped separately, because it needs user roles and features listed.
Will you change anything in our account?
No changes are made without written approval. The review role is read-only.
Related guides
Get a fixed fee for AWS penetration testing
Tell us how many accounts and which services you run. We reply with a written scope, a fee and the policy references.
Get my estimate