Service
Thick client penetration testing for desktop applications
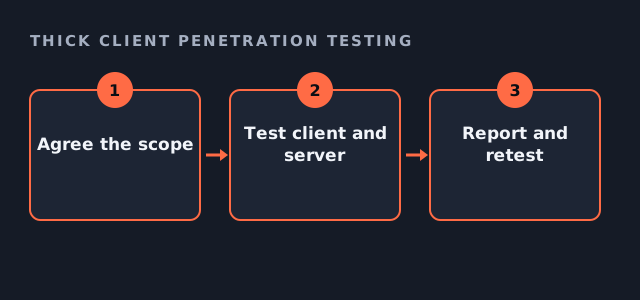
Thick client penetration testing examines desktop software that does real work on the user's machine. So it covers the client, its local data and how it talks to your servers.
- Named tester before day one
- One retest within 30 days
- OWASP WSTG and NIST SP 800-115
Why thick client penetration testing is its own service
Desktop applications keep logic and data on the device. Therefore an attacker with the client in hand can study it at leisure, which web testing alone does not reflect.
Many such products serve finance, healthcare or industry. Also, they often connect to older back-end services that deserve attention too.
What thick client penetration testing examines
The test follows data from the screen to the server. For example, what the client stores, what it trusts and what it sends.
- Local storage of credentials and data
- Communication with back-end services
- Authorisation enforced on the server, not only the client
- Update and installation mechanisms
- Dependence on local privileges
Thick client penetration testing readiness check
Tick what you can provide. Each item speeds up scoping.
Your result appears here as you tick, so you can see what is still open.
Scoping thick client penetration testing
Scope depends on the client's architecture. However, a few questions settle most of it.
| Question | Effect on scope |
|---|---|
| Two-tier or three-tier design? | Direct database access widens scope |
| Which operating systems? | Each platform adds effort |
| Which back-end services? | APIs are tested alongside the client |
| How many user roles? | More roles mean more authorisation checks |
Authorisation and safety
Testing runs only under your written authorisation, inside agreed rules of engagement. Also, a non-production environment is preferred, because desktop tests can change data.
Findings come with evidence and a fix. As a result, your engineers can reproduce and close each issue. Guidance such as the OWASP Desktop App Security Top 10 helps frame them.
Fees and timing
Desktop work is priced after scoping. Most companies land between $10,000 and $30,000, and the exact figure follows scope. One retest within 30 days is included, and a named tester is confirmed before day one. Hands-on testing typically runs 3 to 10 days, depending on scope.
Thick client penetration testing questions
What is thick client penetration testing?
Testing of desktop software that processes data locally, together with its server connections.
Does thick client penetration testing include the API?
Usually yes, because the client's server calls are part of the risk.
Can thick client penetration testing run in production?
It can, but a test environment is safer, because tests may change data.
Is a retest included?
Yes. One retest within 30 days is included.
Related guides
Scope your thick client penetration testing
Tell us about the client, its platforms and its back end. We reply with a written estimate, usually within four working hours.
Get my estimate